Vulnerabilities
2026-11-07 · 2 d ago
Source: The Hacker News
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot
Summary
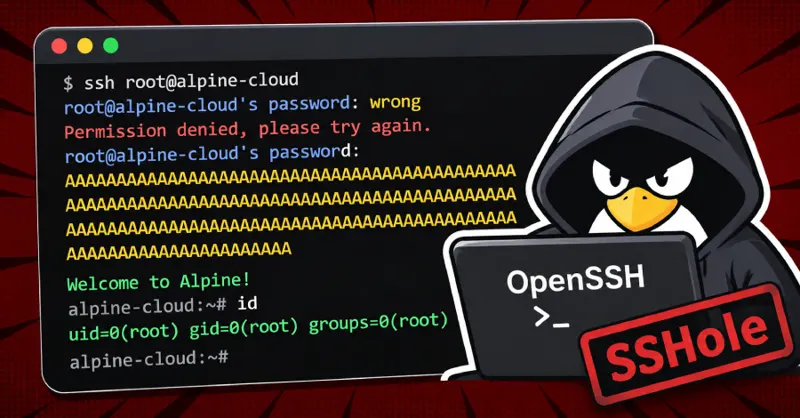
Threat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that have no password set, according to Previdian. The vulnerability, tracked as CVE-2026-123158 (CVSS score: 8.1) and codenamed SSHole (or *sshole), impacts Linux systems that run OpenSSH on the musl C library with Pluggable Authentication Modules (PAM) disabled,
For more information, read the full story at the original source: The Hacker News ↗
Vulnerabilities in this story
Also reported by
- SecurityWeek: Hackers Exploiting ‘SSHole’ Authentication Bypass in OpenSSH ↗
- BleepingComputer: Hackers exploit SSHole OpenSSH flaw to breach Linux systems ↗
- ZDNet How-to: Alpine Linux and OpenSSH patch flaw that’s as bad as it can get ↗
- Help Net Security: OpenSSH flaw exploited in the wild just hours after disclosure (CVE-2026-123158) ↗