Vulnerabilities
2026-11-19 · 2 d ago
Source: The Hacker News
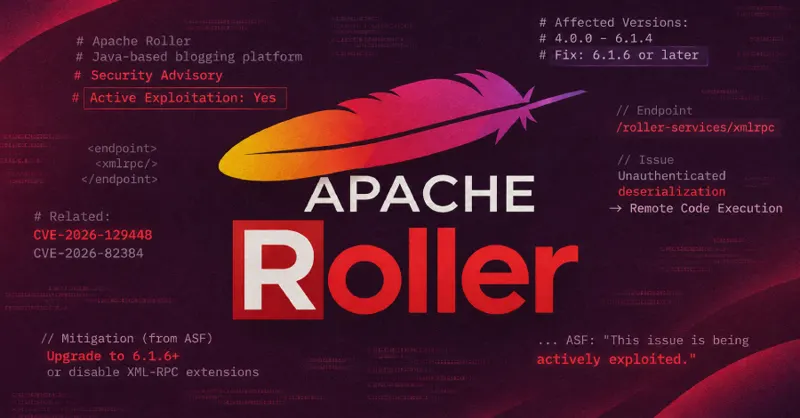
Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
Summary
A critical security flaw in Apache Roller, an open-source, Java-based blogging platform, has come under active exploitation in the wild, according to the Apache Software Foundation (ASF) The vulnerability, tracked as CVE-2026-129448 (CVSS score: 9.8), is a case of unauthenticated deserialization in the XML-RPC endpoint that could lead to remote code execution. "Deserialization of Untrusted
For more information, read the full story at the original source: The Hacker News ↗