Vulnerabilities
2026-11-13 · just now
Source: The Hacker News
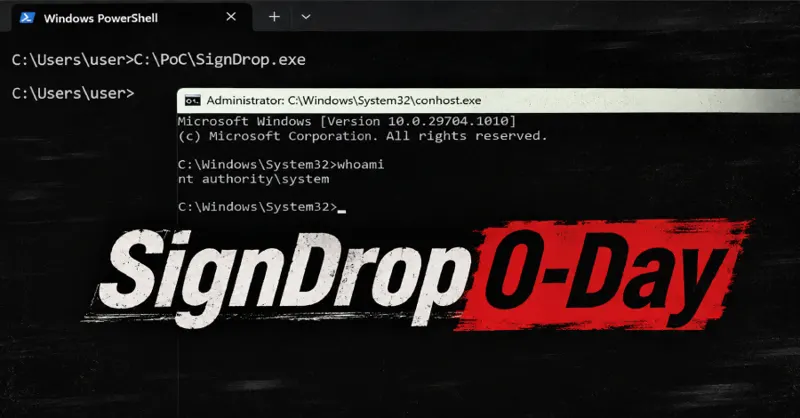
New SignDrop Zero-Day Exploit Turns Windows CLFS Security Feature Into SYSTEM Access
New SignDrop Zero-Day Exploit Turns Windows CLFS Security Feature Into SYSTEM Access
Summary
Public exploit code released earlier this week claims that a local Windows user can gain SYSTEM privileges through the Common Log File System driver. The proof of concept, called SignDrop, targets a log-authentication feature added to the driver last year. It abuses how clfs.sys creates companion files when a privileged process opens a prepared log, using path redirection to take control of
For more information, read the full story at the original source: The Hacker News ↗