Vulnerability details
CVE-2026-123039
Actively exploitedLocal privilege escalation to root in the DynamicCLI daemon via local world-writable control socket
Remedy
Required action (CISA): Apply mitigations in accordance with vendor instructions, ensuring compliance with CISA's BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA's "Forensics Triage Requirements" (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. (due: 2026-11-16)
Official description
The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating connecting processes. An authenticated local user can send a command to the socket and have it executed as root.
Related news
-
 The firewall becomes the foothold: Attackers turn Check Point gateways against customers
Network World · 1 h ago
-
 Hackers Exploit PHP2Shell Flaws in Check Point Gateways to Deploy TSGA Backdoor and Wipe ESXi Files
The Hacker News · 13 h ago
-
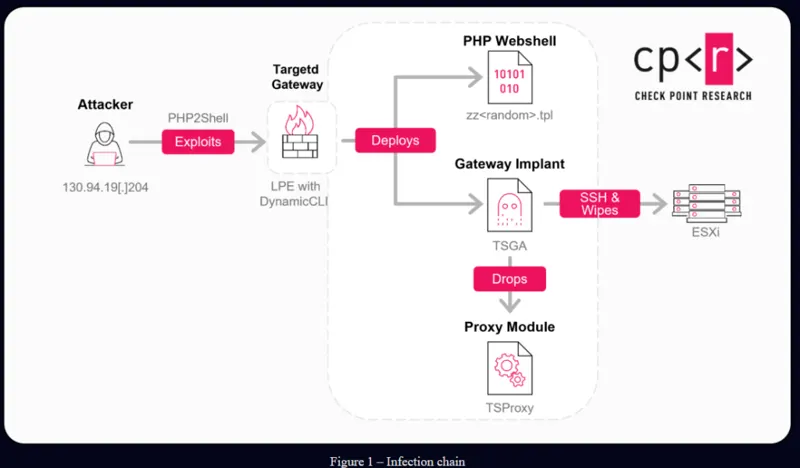 Unpatched Check Point Gateways Are Being Wiped exploiting PHP2Shell
Security Affairs · 15 h ago
-
 Check Point gateways hacked via PHP2Shell to deploy VMware ESXi wiper
BleepingComputer · 15 h ago
-
 PHP2Shell Exploited in Destructive Check Point Gateway Attacks
SecurityWeek · 19 h ago
CVSS scores
| Score | Version | Source | Vector |
|---|---|---|---|
| 7.8High | 3.1 | CVEProject cvelistV5 (CNA) (checkpoint) | CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H |
Affected products
| Vendor | Product | Versions | Source |
|---|---|---|---|
| checkpoint | Quantum Security Gateway | R81.20 with Jumbo Hotfix Take 173 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Gateway | R82 with Jumbo Hotfix Take 130 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Gateway | R82.10 with Jumbo Hotfix Take 50 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Gateway | R82.20 with Jumbo Hotfix Take 10 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Management | R81.20 with Jumbo Hotfix Take 173 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Management | R82 with Jumbo Hotfix Take 130 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Management | R82.10 with Jumbo Hotfix Take 50 or below | CVEProject cvelistV5 (CNA) |
| checkpoint | Quantum Security Management | R82.20 with Jumbo Hotfix Take 10 or below | CVEProject cvelistV5 (CNA) |
References and advisories
2Details
- Published
- 2026-11-12
- Last updated
- 2026-11-14
- State
- Published
- Assigner (CNA)
- checkpoint
- Kolun priority
- 74 · High
CISA KEV catalog
- Date added
- 2026-11-13
- Due date
- 2026-11-16
- Used in ransomware
- Unknown
Exploit prediction (EPSS)
SSVC assessment (CISA)
- Automatable
- No
- Exploitation
- Active
- Technical impact
- Total
Weaknesses (CWE)
- CWE-862Missing Authorization.
- CWE-732Incorrect Permission Assignment for Critical Resource.