Vulnerability details
CVE-2026-123007
NGINX ngx_http_v2_module vulnerability
Remedy
- NGINX Plus — version 37.3.0.1 and later
- NGINX Plus — version 37.0.8.1 and later
- NGINX Open Source — version 1.31.9 and later
- NGINX Open Source — version 1.30.7 and later
Workaround: None
Official description
This issue affects NGINX Plus or NGINX Open Source configurations that use HTTP/2. When NGINX processes undisclosed traffic, the flow control window can exceed the allowed threshold, potentially resulting in a heap buffer overflow typically followed by an NGINX worker segmentation fault. Additionally, attackers can execute code on systems with Address Space Layout Randomization (ASLR) disabled or when the attacker can bypass ASLR. Impact: An attacker could leverage this vulnerability to crash the NGINX worker process, corrupt its memory, or potentially execute code remotely. There is no control plane exposure; this is a data plane issue only. Note: Software versions which have reached End of Technical Support (EoTS) are not evaluated.
Related news
-
 Navigating Vulnerability Hysteria in the AI Era
Dark Reading · 1 d ago
-
 NGINX2Root: F5 patches five critical NGINX vulnerabilities
Help Net Security · 1 d ago
-
 F5 Patches Critical NGINX2Root Flaws as PoC Exploits Go Public
SecurityWeek · 1 d ago
-
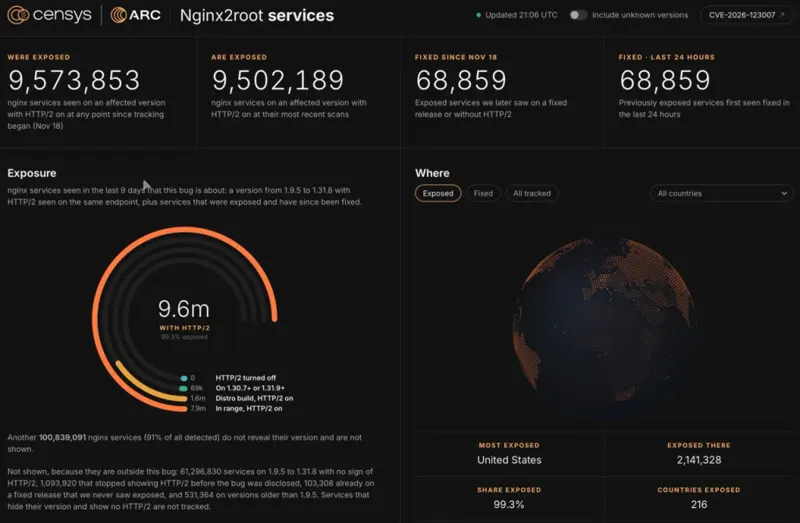 nginx2root:AI Discovers Five Critical nginx Flaws and a Path to Root
Security Affairs · 1 d ago
-
 10-Year-Old NGINX HTTP/2 Flaw Lets Unauthenticated Attackers Execute Code on Servers
The Hacker News · 2 d ago
CVSS scores
| Score | Version | Source | Vector |
|---|---|---|---|
| 9.2Critical | 4.0 | CVEProject cvelistV5 (CNA) (f5) | CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N |
| 8.1High | 3.1 | CVEProject cvelistV5 (CNA) (f5) | CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H |
Affected products
| Vendor | Product | Versions | Source |
|---|---|---|---|
| F5 | NGINX Open Source | 1.30.0 ≤ v < 1.30.7 | CVEProject cvelistV5 (CNA) |
| F5 | NGINX Open Source | 1.31.0 ≤ v < 1.31.9 | CVEProject cvelistV5 (CNA) |
| F5 | NGINX Open Source | 1.9.5 ≤ v | CVEProject cvelistV5 (CNA) |
| F5 | NGINX Plus | 37.0.0 ≤ v < 37.0.8.1 | CVEProject cvelistV5 (CNA) |
| F5 | NGINX Plus | 37.1.0 ≤ v < 37.3.0.1 | CVEProject cvelistV5 (CNA) |
| F5 | NGINX Plus | R33 ≤ v | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Cloud Device (IECD) | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Device Kit - arm64 | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Device Kit - x86-64 | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Hub | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Management Cloud | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Management Pro V1 | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Management Pro V2 | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Management Virtual | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Own Device (IEOD) | All | CVEProject cvelistV5 (CNA) |
| Siemens | Industrial Edge Virtual Device (IEVD) | All | CVEProject cvelistV5 (CNA) |
References and advisories
17- https://my.f5.com/manage/s/article/K000163926 vendor-advisorypatch
- https://www.wiz.io/blog/nginx-http2-rce-vulnerabilities
- https://news.ycombinator.com/item?id=50547374
- https://github.com/nginx/nginx/commit/b89c4100bf6762a45e4a6463eaf4b70368277c94
- https://ubuntu.com/security/CVE-2026-123007
- https://github.com/advisories/GHSA-m4q8-cf44-f42r
- https://github.com/openresty/openresty/issues/1165
- https://github.com/nginx/nginx/issues/2002
- https://nginx.org/en/CHANGES
- https://github.com/chainguard-forks/ingress-nginx/pull/69
- https://cyberscoop.com/nginx-critical-vulnerabilities-exploits/
- https://www.rapid7.com/blog/post/ve-cve-2026-123007-critical-nginx-http-2-integer-underflow-leads-to-rce-fixed/
- https://xint.io/blog/nginx2root-remote-code-execution
- https://nginx2root.com
- https://access.redhat.com/security/cve/cve-2026-123007
- https://github.com/Azure/aks-app-routing-operator/issues/623
- https://cert-portal.siemens.com/productcert/html/ssa-935812.html
Details
- Published
- 2026-11-18
- Last updated
- 2026-11-20
- State
- Published
- Assigner (CNA)
- f5
- Kolun priority
- 47 · Medium
Exploit prediction (EPSS)
SSVC assessment (CISA)
- Automatable
- No
- Exploitation
- None
- Technical impact
- Total
Weaknesses (CWE)
- CWE-191Integer Underflow (Wrap or Wraparound)
- CWE-787Out-of-bounds Write