Vulnerability details
CVE-2026-116331
PostgreSQL
PostgreSQL min/max aggregate type confusion executes arbitrary code
CVSS 3.1
8.8High
Remedy
Versions not listed as affected in the CVE record:
- PostgreSQL — version 18.7 and later
- PostgreSQL — version 17.12 and later
- PostgreSQL — version 16.16 and later
- PostgreSQL — version 15.20 and later
- PostgreSQL — version 14.25 and later
Official description
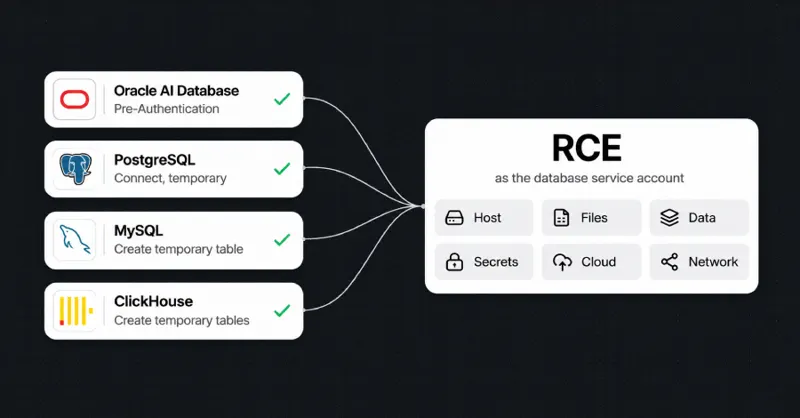
Type confusion in PostgreSQL min/max aggregate optimization allows an object creator to execute arbitrary code as the operating system user running the database, via a user-defined aggregate whose SORTOP option causes the planner to treat the aggregate's input and result as the same type when they differ. Versions before PostgreSQL 18.7, 17.12, 16.16, 15.20, and 14.25 are affected.
Related news
CVSS scores
| Score | Version | Source | Vector |
|---|---|---|---|
| 8.8High | 3.1 | CVEProject cvelistV5 (CNA) (PostgreSQL) | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H |
Affected products
| Vendor | Product | Versions | Source |
|---|---|---|---|
| — | PostgreSQL | v < 14.25 | CVEProject cvelistV5 (CNA) |
| — | PostgreSQL | 15 ≤ v < 15.20 | CVEProject cvelistV5 (CNA) |
| — | PostgreSQL | 16 ≤ v < 16.16 | CVEProject cvelistV5 (CNA) |
| — | PostgreSQL | 17 ≤ v < 17.12 | CVEProject cvelistV5 (CNA) |
| — | PostgreSQL | 18 ≤ v < 18.7 | CVEProject cvelistV5 (CNA) |
References and advisories
1
Kolun on Telegram @kolunsec
Exploited CVEs, key news and a daily digest
Alerts for this product's next CVEsFollow the product to get new vulnerabilities on Telegram.
Details
- Published
- 2026-11-12
- Last updated
- 2026-11-13
- State
- Published
- Assigner (CNA)
- PostgreSQL
- Kolun priority
- 26 · Low
Exploit prediction (EPSS)
0.59%
Probability of exploitation in 30 days
49.1%
Percentile (among all CVEs)
SSVC assessment (CISA)
- Automatable
- No
- Exploitation
- None
- Technical impact
- Total
Weaknesses (CWE)
- CWE-843Access of Resource Using Incompatible Type ('Type Confusion')