Vulnerability details
CVE-2026-101786
Oracle MySQL ClusterOracle MySQL Server
CVSS 3.1
7.2High
Official description
Vulnerability in the MySQL Server, MySQL Cluster product of Oracle MySQL (component: Server: Optimizer). Supported versions that are affected are MySQL Server: 26.7.0-26.7.1; MySQL Cluster: 26.7.0-26.7.1. Easily exploitable vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server, MySQL Cluster. Successful attacks of this vulnerability can result in takeover of MySQL Server, MySQL Cluster. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H).
Related news
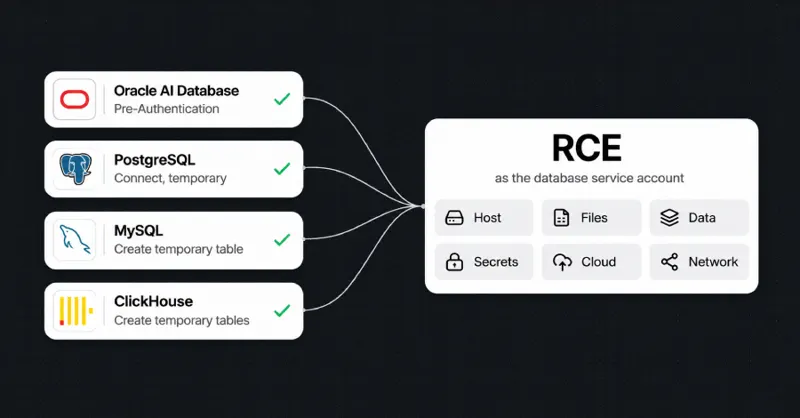
CVSS scores
| Score | Version | Source | Vector |
|---|---|---|---|
| 7.2High | 3.1 | CVEProject cvelistV5 (CNA) (oracle) | CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H |
Affected products
| Vendor | Product | Versions | Source |
|---|---|---|---|
| Oracle Corporation | MySQL Cluster | 26.7.0-26.7.1 | CVEProject cvelistV5 (CNA) |
| Oracle Corporation | MySQL Server | 26.7.0-26.7.1 | CVEProject cvelistV5 (CNA) |
References and advisories
1- https://www.oracle.com/security-alerts/cpuoct2026.html vendor-advisory
Kolun on Telegram @kolunsec
Exploited CVEs, key news and a daily digest
Alerts for this product's next CVEsFollow the product to get new vulnerabilities on Telegram.
Details
- Published
- 2026-10-21
- Last updated
- 2026-10-22
- State
- Published
- Assigner (CNA)
- oracle
- Kolun priority
- 30 · Low
Exploit prediction (EPSS)
0.43%
Probability of exploitation in 30 days
38.1%
Percentile (among all CVEs)
SSVC assessment (CISA)
- Automatable
- No
- Exploitation
- None
- Technical impact
- Total
Weaknesses (CWE)
- CWE-284Improper Access Control